Thailand’s Personal Data Protection Act B.E. 2562 (2019) (PDPA) became fully effective and enforceable on June 1, 2022. To ensure that the PDPA will be smoothly and efficiently enforced, the Personal Data Protection Commission (PDPC) is issuing various subordinate regulations. On June 20, 2022, the first set of these regulations was issued and published in the Government Gazette, and according to the Ministry of Digital Economy and Society (MDES), another set of subordinate regulations is expected to be issued by the end of June 2022.
The first set consists of the following four subordinate regulations:
1) Notification of the PDPC Re: Exemption to the Record of Processing Activities Requirement for Data Controllers that Are Small Businesses B.E. 2565 (2022) (“ROPA Exemption Notification”)
Under the PDPA, data controllers are obligated to prepare and maintain a record of processing activities (ROPA) containing information specified in Section 39 of the PDPA, including the personal data collected, the purposes of the processing of the personal data, the retention period, etc.
However, under this ROPA Exemption Notification, a data controller will be exempted from the obligation to prepare and maintain a record of such required information (except information related to the rejection of a request from a data subject to exercise (i) right of access; (ii) right to data portability; (iii) right to object; and (iv) right to rectification), if its business falls within the scope of any of the following:
- Small or medium-sized business according to the law on small and medium-sized enterprise promotion, defined as follows:
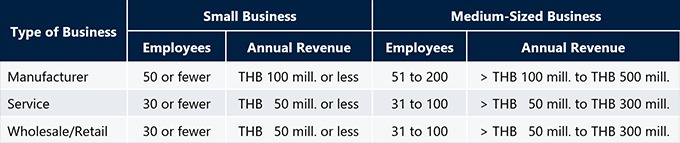
- Community enterprise or social enterprise, as referred to under the law on community enterprise promotion.
- Social enterprise, as referred to under the under the law on social enterprise promotion.
- Cooperative, cooperative union, or agriculturist’s group under the law on cooperatives.
- Foundation, association, religious body, or non-profit organization.
- Household business or other business of the same nature.
- Internet cafe service provider.
This exemption will not apply to small businesses in certain circumstances, such as when the processing of personal data is required by law related to a computer crime to retain computer traffic data, when it involves personal data having a risk of affecting the rights and freedom of an individual, or when the data controller processes the personal data on a regular basis.
The ROPA Exemption Notification came into force on June 21, 2022.
2) Notification of the PDPC Re: Rules and Procedures for the Preparation and Maintenance of the Record of Processing Activities by the Data Processor B.E. 2565 (2022) (“Data Processor Notification”)
The PDPA also imposes an obligation on data processors to prepare and maintain a ROPA, without further explanation. With the enactment of the Data Processor Notification, it is now clear that the data processor must ensure that its ROPA will include at least the following information:
- Information on the data processor;
- Information on the local representative of the data processor (if any);
- Information on and contact details of the data protection officer (if any);
- Information on the data controller on whose behalf or pursuant to whose instruction the data processor acts, and on the local representative of the data controller (if any);
- Types or characteristics of the collection, use, or disclosure of personal data conducted by the data processor on behalf of or pursuant to the instruction of the data controller, including the category of personal data and purpose of the collection, use, or disclosure;
- If personal data is transferred outside of Thailand, the category of the person or entity receiving the personal data; and
- A description of the security measures implemented by the data processor.
The ROPA must be maintained in written or electronic form, and must be easily accessible and promptly available for inspection by the Office of the PDPC, the data controller, or their designated person, when requested.
The Data Processor Notification will only become enforceable 180 days after the date of publication in the Government Gazette, i.e., December 17, 2022. Therefore, data processors are given a grace period to prepare themselves to be in compliance with this ROPA requirement.
3) Notification of the PDPC Re: Security Measures of the Data Controller B.E. 2565 (2022) (“Security Measures Notification”)
The minimum required security standards prescribed by the Security Measures Notification are generally in alignment with the previous Notification of the MDES on Security Measures which ceased effectiveness on May 31, 2022 (“MDES Notification”). Data controllers who have prepared themselves to be in compliance with the MDES Notification will therefore find it easy to comply with the Security Measures Notification, which took effect on June 21, 2022.
The key requirements under the Security Measures Notification include the following:
- Data controllers must ensure that security measures will be applied to personal data in any form whatsoever.
- Data controllers must ensure that security measures consist of appropriate organizational measures and technical measures, which may also include physical measures, if necessary, whereby the level of risk and possibility of occurrence of data breach incidents and the consequences of data breach incidents are taken into consideration.
- When preparing the security measures, the data controller must consider the identification of possible risk to significant information assets, prevention of the occurrence of significant risk, monitoring of threats and data breach incidents, encounters with threats and data breach incidents, risk treatment, and recovery, as appropriate and in accordance with the level of risk.
- Data controllers must be able to maintain the confidentiality, integrity, and availability of personal data as appropriate and in accordance with the level of risk, taking into account technological factors, context, circumstances, and standards accepted by similar types of businesses.
- Security measures for personal data in electronic form must cover the components of the relevant information system such as servers, clients, storage system and devices, software, etc., as appropriate and in accordance with the level of risk.
- Security measures in relation to the access, use, alteration, modification, deletion, or disclosure of personal data are substantially similar to the requirements under the MDES Notification – for example, access control, user access management, user responsibilities, audit trails, etc. However, the Security Measures Notification sets forth further requirements.
Apart from the above, the Security Measures Notification also requires the data controller to: (i) build privacy and security awareness for its personnel and users; (ii) review security measures when necessary or when there is a change in technology or a data breach incident; and (iii) set requirements on security measures for its data processor.
4) Notification of PDPC Re: Rules for the Consideration of the Imposition of Administrative Penalties by the Expert Committee B.E. 2565 (2022) (“Administrative Penalties Notification”)
In addition to imposing administrative fines on the offender, the Expert Committee which will be appointed under the PDPA will also be empowered to issue orders on the enforcement of administrative penalties, including seizure, confiscation, and sale by auction.
The key points of the Administrative Penalties Notification, which took effect on June 21, 2022, are as follows:
- In determining the administrative fine or administrative measure, the Expert Committee is to consider certain factors such as whether the offense was committed willfully or out of gross negligence, the severity of the offense, the size of the business, the benefits which the data subject will receive if the administrative measures are enforced against the offender, the value of damages, the level of responsibility and standards at the time of commission of the offense, etc. One of the crucial factors that will be considered by the Expert Committee is the record of administrative fines or administrative measures already imposed or enforced on the offender and, if the offender is a legal entity, on the person associated with such legal entity.
- The Administrative Penalties Notification categorizes offenses into two categories, non-serious offenses and serious offenses, which are treated differently by the Expert Committee.
Non-Serious Offense:
The Expert Committee may issue the following orders to the data controller, data processor, or other related person:
– Warning or order to the offender to rectify, cease, suspend, refrain or abstain from the violation or non-compliance with the PDPA within the time specified.
– Order to prohibit the offender from causing any damage to the data subject, or to perform any act to remedy the damages.
– Order to restrict the collection, use, or disclosure of personal data upon which an offense has been committed in order to remedy damages within the time specified.
In addition to the above, the Expert Committee may set forth conditions or procedures for the improvement of personnel, process, or technology to ensure its efficacy and suitability as the Expert Committee deems appropriate.
Serious Offense:
The Expert Committee shall impose administrative penalties on the data offender by taking into account the severity of the offense and other circumstances as deemed appropriate.
The Expert Committee may also issue orders similar to those for the non-serious offense.
- If an administrative fine has been imposed on the offender and the offender failed to make payment within the time specified, the Expert Committee may issue a warning to the offender to make such payment within a period of not less than seven days, and if the offender still fails to make such payment in full, the provisions of the administrative procedures law will be applied.
It is vital to note that any failure to comply with the requirements under these subordinate regulations may lead to the data controller or data processor being subject to penalties specified under the PDPA, depending on the violation.